Ready when someone asks for proof
Insurers, auditors, big customers and inspectors all ask the same thing: show us what you do to protect the business. Tachi keeps the yearly security assessment, training records and the gaps you're fixing on one screen, and it's one download when they ask. On the healthcare plan it adds the HIPAA risk assessment, business associate agreements and expiring licenses.
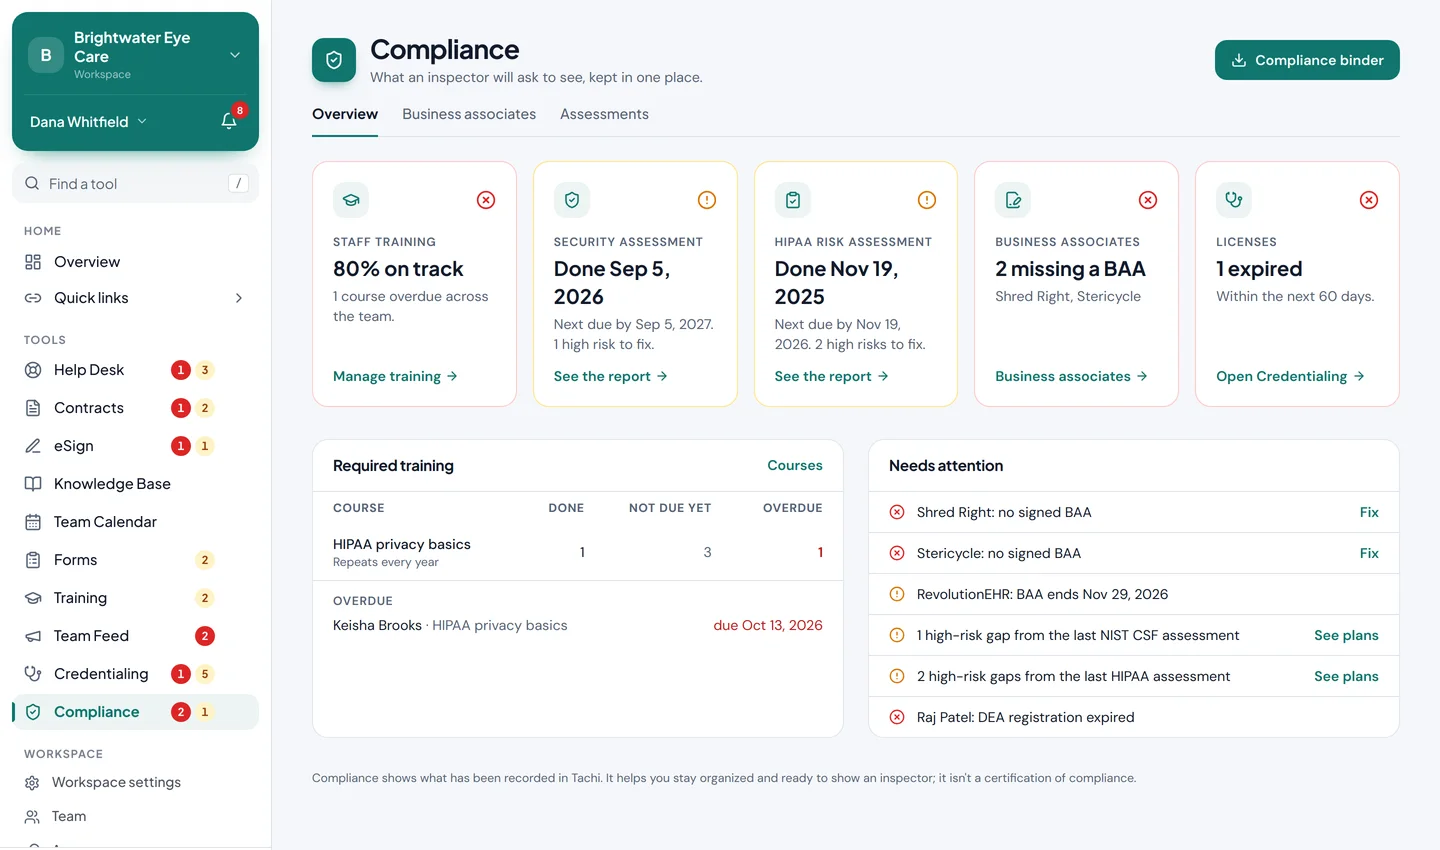
Training that repeats itself
Set a course like security awareness to repeat every year, for everyone or for a group. Record in-person classes with a printable sign-in sheet. Every completion is kept as proof, year after year.
One download when they ask
The compliance binder bundles a summary, each assessment's report with its open gaps, and training records. On the healthcare plan it adds the list of business associates with their signed BAAs, and expiring licenses.
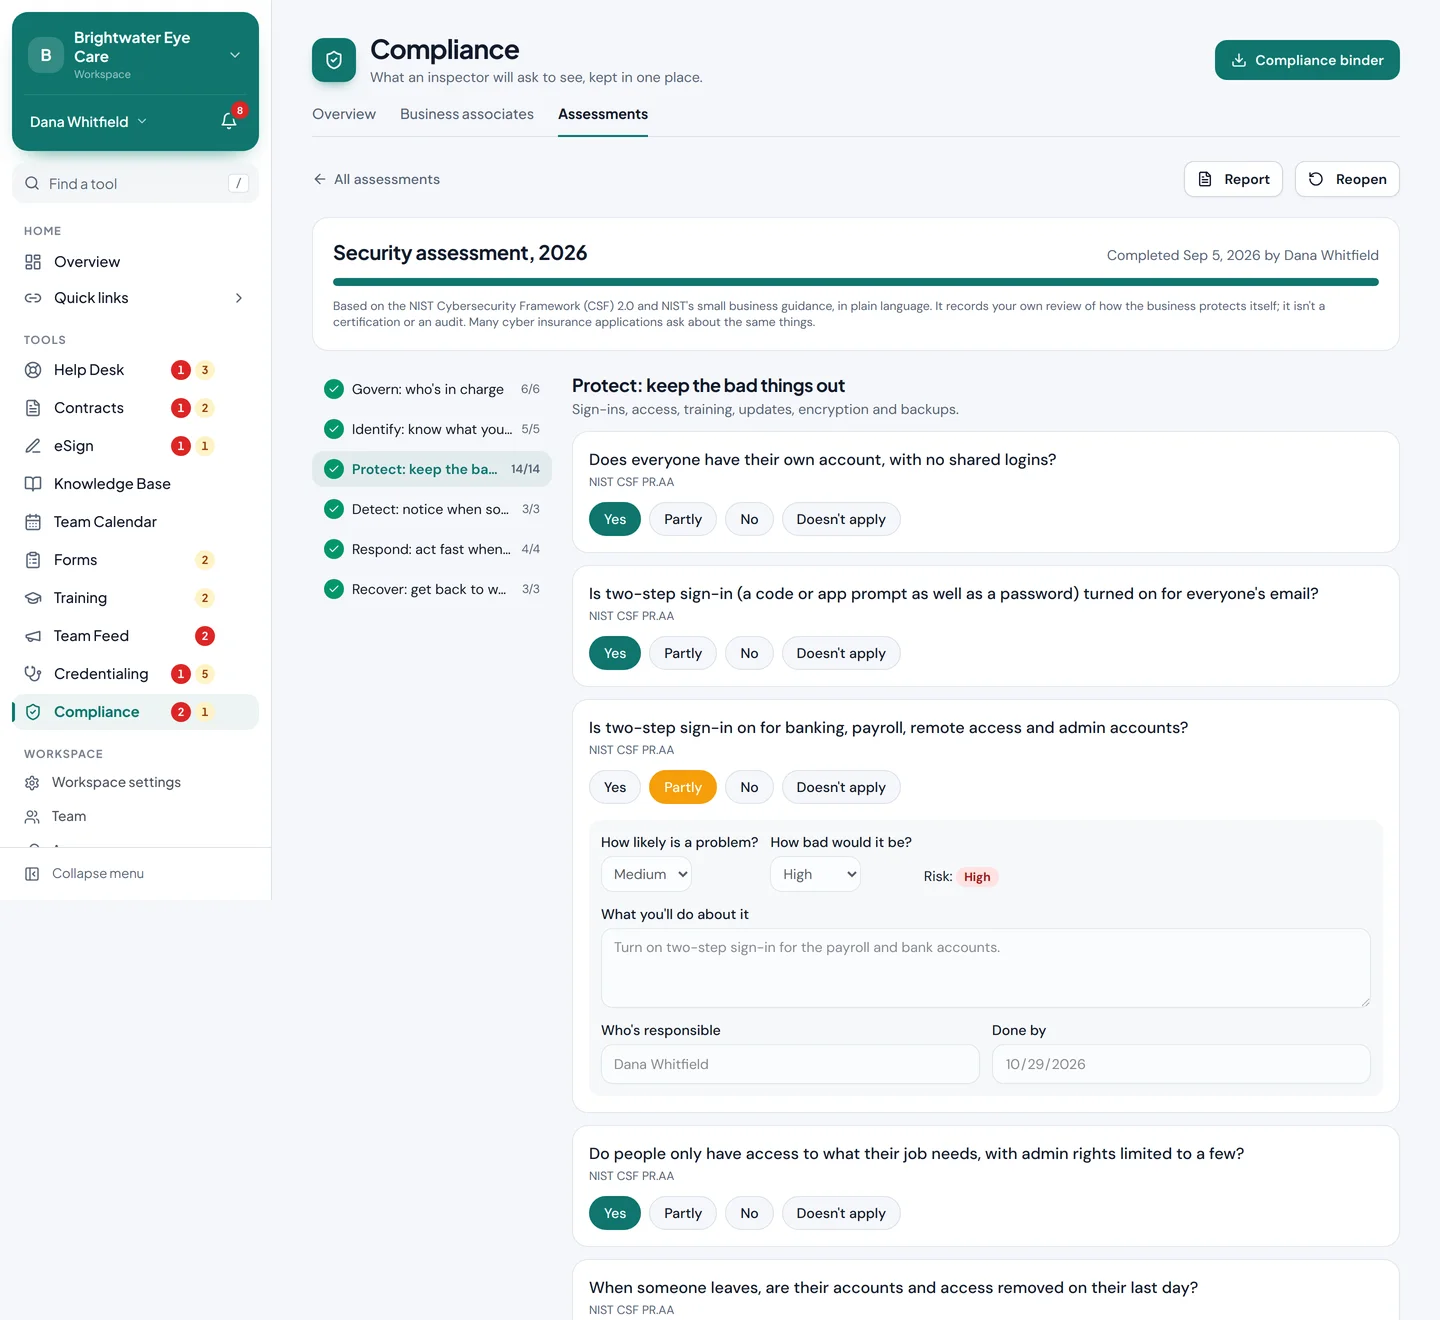
A yearly security check, in plain words
About 35 questions across the six parts of the NIST Cybersecurity Framework: who's in charge, knowing what you have, protecting it, noticing problems, responding and recovering. For anything that isn't fully in place, rate the risk and write down who will fix it and by when. Next year starts from this year's answers, and cyber insurance applications ask about many of the same things.
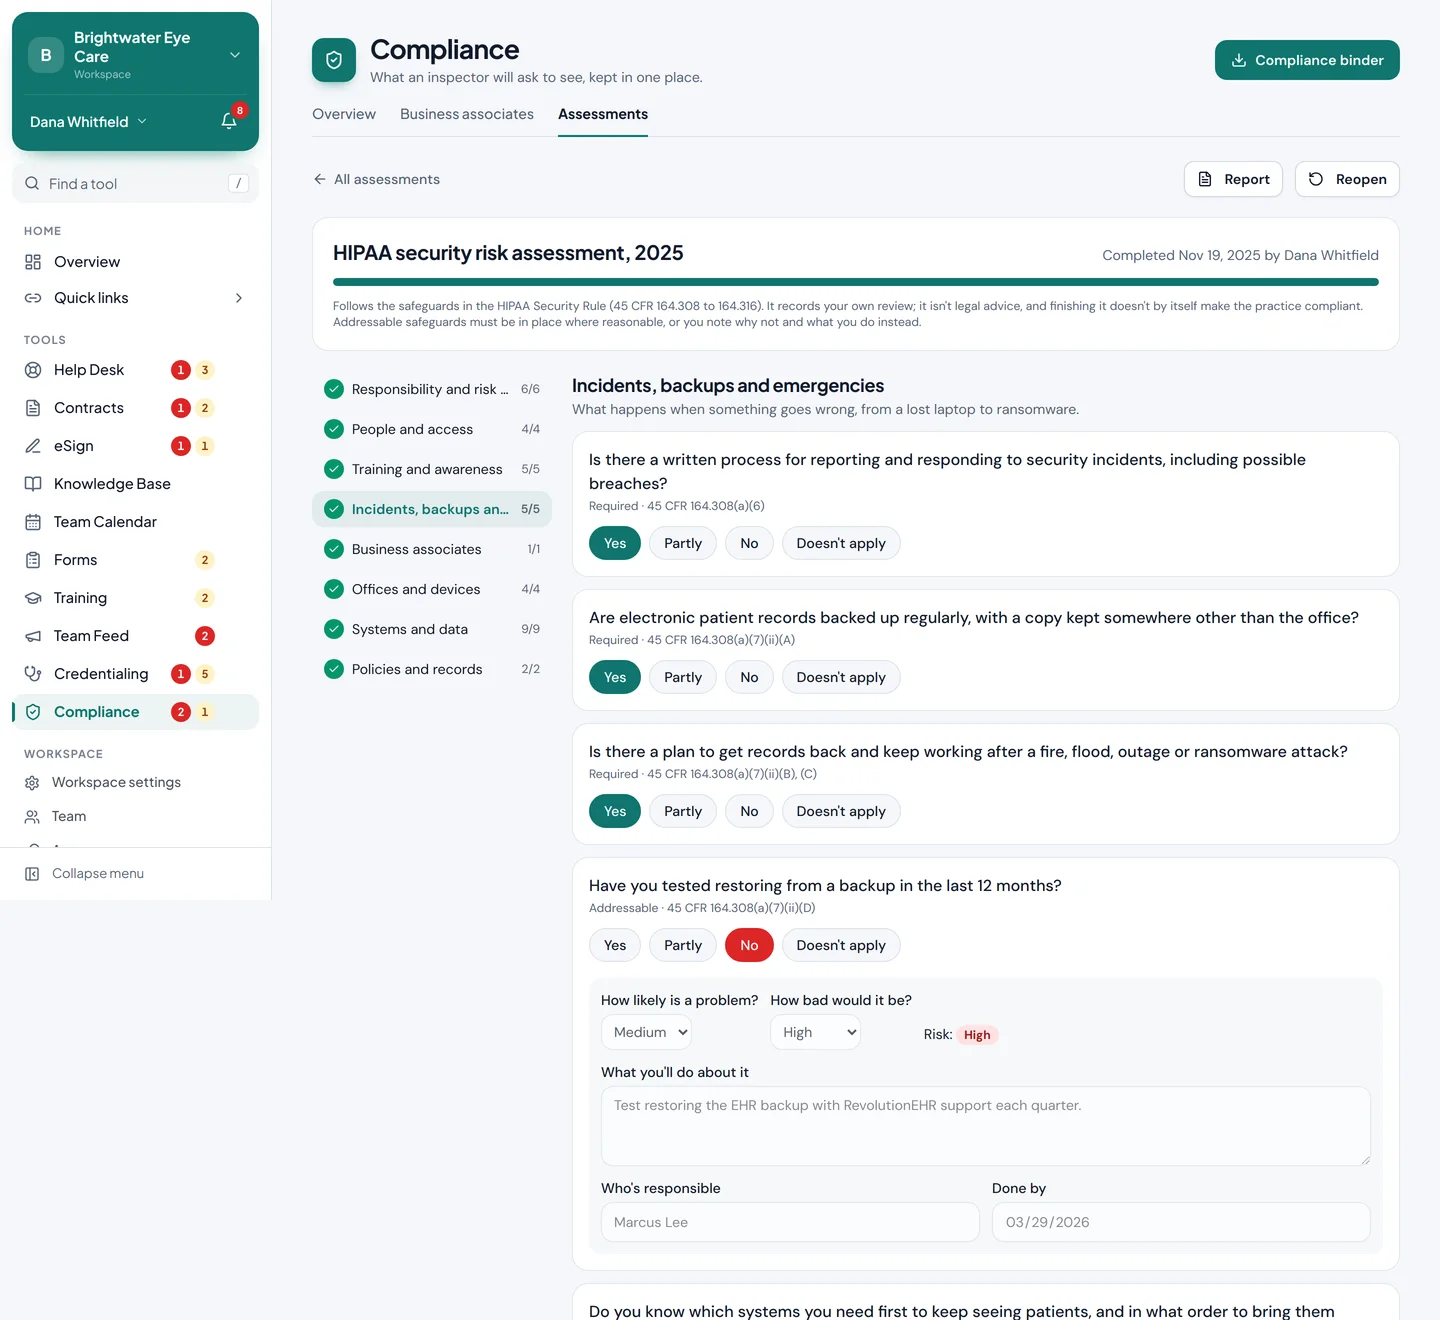
On the healthcare plan: HIPAA, done properly
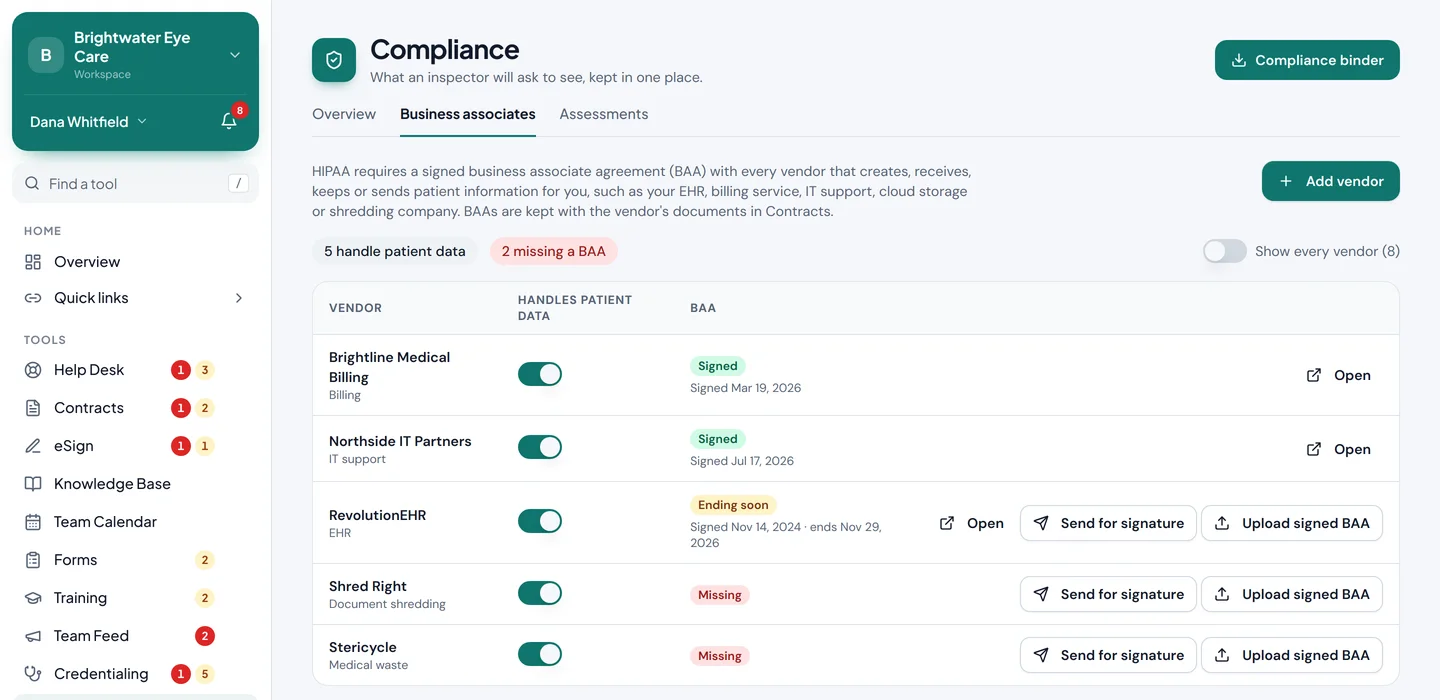
Walk through each safeguard in the HIPAA Security Rule for the yearly risk assessment practices are required to do. Mark the vendors that handle patient information and see which have a signed BAA. Send one for signature with eSign, and the signed copy is filed under the vendor automatically.
Also in Compliance
- Overdue training at a glance
- High-risk gaps are flagged until they're fixed
- Printable assessment reports
- Every change is in the audit log
Try Compliance with your team this week.
Set up in minutes. Free for 14 days, no card needed.
Start your free trial